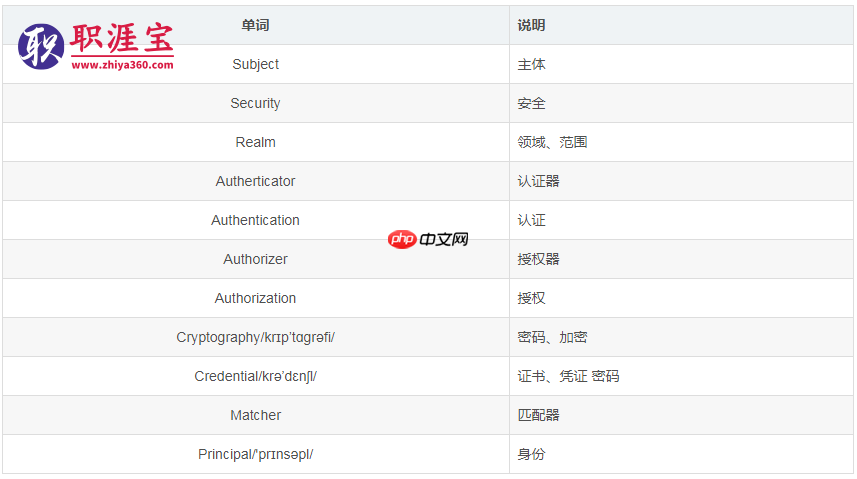
apache shiro是一个强大且易用的java安全框架,用于执行身份验证、授权、密码和会话管理。通过shiro的易于理解的api,您可以快速、轻松地为任何应用程序提供安全性,从最小的移动应用程序到最大的网络和企业应用程序。
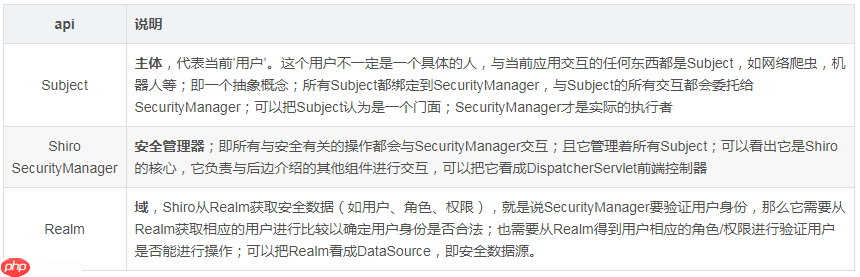
Shiro的官方网站提供了详细的框架图和架构说明。从外部来看,Shiro框架的核心是Subject,应用代码直接与Subject交互。Shiro的对外API主要围绕Subject设计。
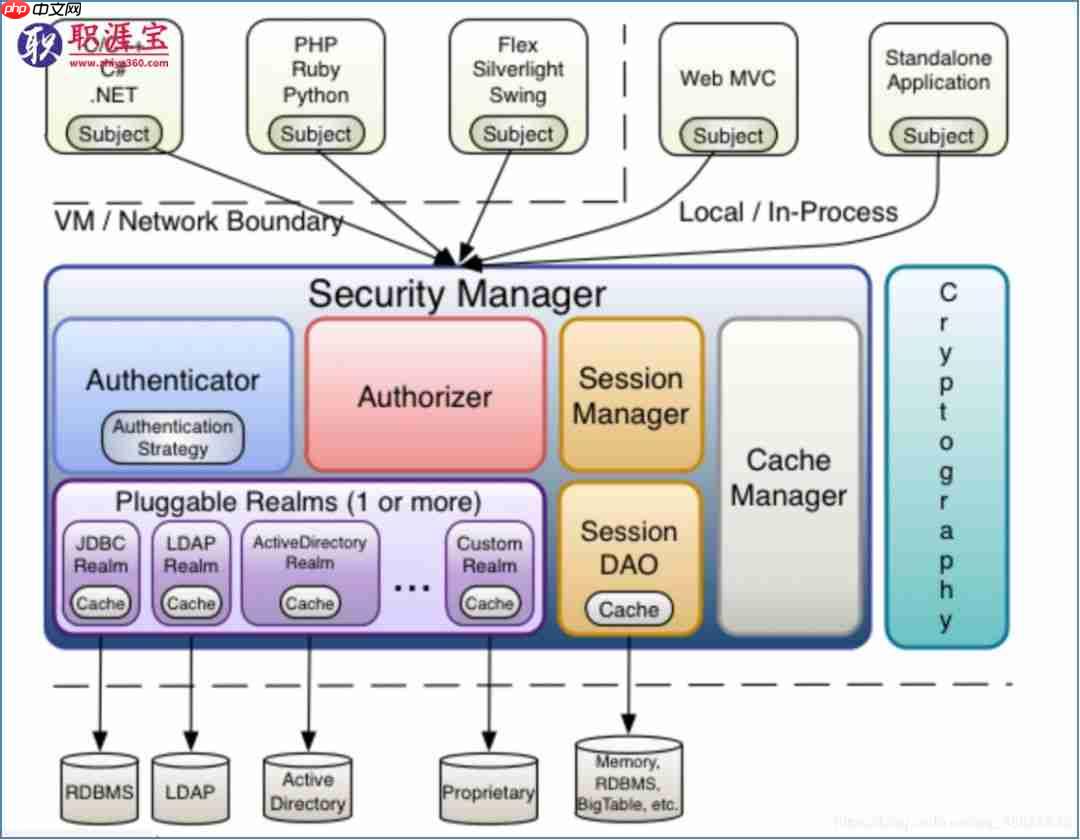
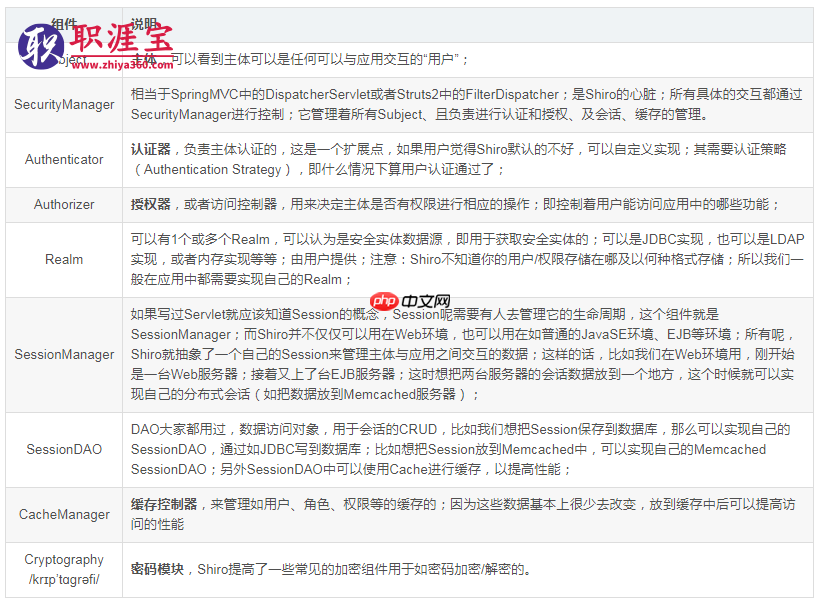
内部结构图显示了Shiro的组件,包括SecurityManager、Authenticator、Authorizer和SessionManager等。这些组件协同工作,确保安全功能的实现。

立即进入“豆包AI人工智官网入口”;
立即学习“豆包AI人工智能在线问答入口”;
在Shiro中,shiro.ini文件用于配置,main部分提供了对根对象SecurityManager及其依赖对象的配置。以下是配置示例:
# 创建对象securityManager=org.apache.shiro.mgt.DefaultSecurityManager
其构造器必须是public空参构造器,通过反射创建相应的实例。配置格式如下:
对象名=全限定类名 # 相对于调用public无参构造器创建对象对象名.属性名=值 # 相当于调用setter方法设置常量值对象名.属性名=$对象引用 # 相当于调用setter方法设置对象引用
users部分用于配置用户/密码及其角色:
[users]zhang=123,role1,role2wang=123
roles部分用于配置角色及权限之间的关系:
[roles]role1=user:create,user:updaterole2=*
如果只有角色没有对应的权限,可以不配置roles。
urls部分用于web,配置web url的拦截规则:
/index.html = anon/admin/** = authc, roles[admin],perms["permission1"]
官方教程的第一个案例展示了如何添加依赖和配置shiro.ini文件。首先,添加依赖:
org.apache.shiro shiro-core 1.1.0 org.slf4j slf4j-simple 1.6.1 test junit junit 4.12 test commons-logging commons-logging 1.2
然后,在src/main/resources下添加shiro.ini文件:
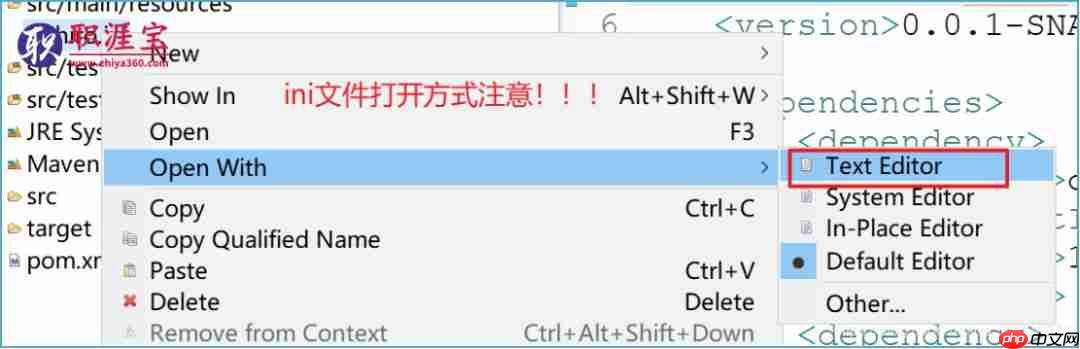
内容如下:
[users]root = 123456 # 账号为root 密码是 123456
认证操作的代码示例:
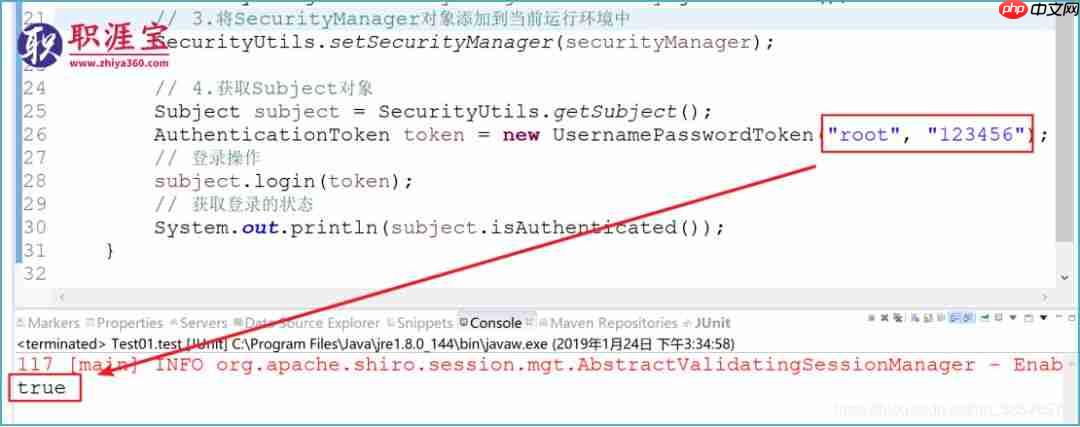
@Testpublic void test() { // 1.获取SecurityManager工厂对象 Factory factory = new IniSecurityManagerFactory("classpath:shiro.ini"); // 2.通过Factory对象获取SecurityManager对象 SecurityManager securityManager = factory.getInstance(); // 3.将SecurityManager对象添加到当前运行环境中 SecurityUtils.setSecurityManager(securityManager); // 4.获取Subject对象 Subject subject = SecurityUtils.getSubject(); AuthenticationToken token = new UsernamePasswordToken("root", "123456"); // 登录操作 subject.login(token); // 获取登录的状态 System.out.println(subject.isAuthenticated());}
测试账号密码正确:
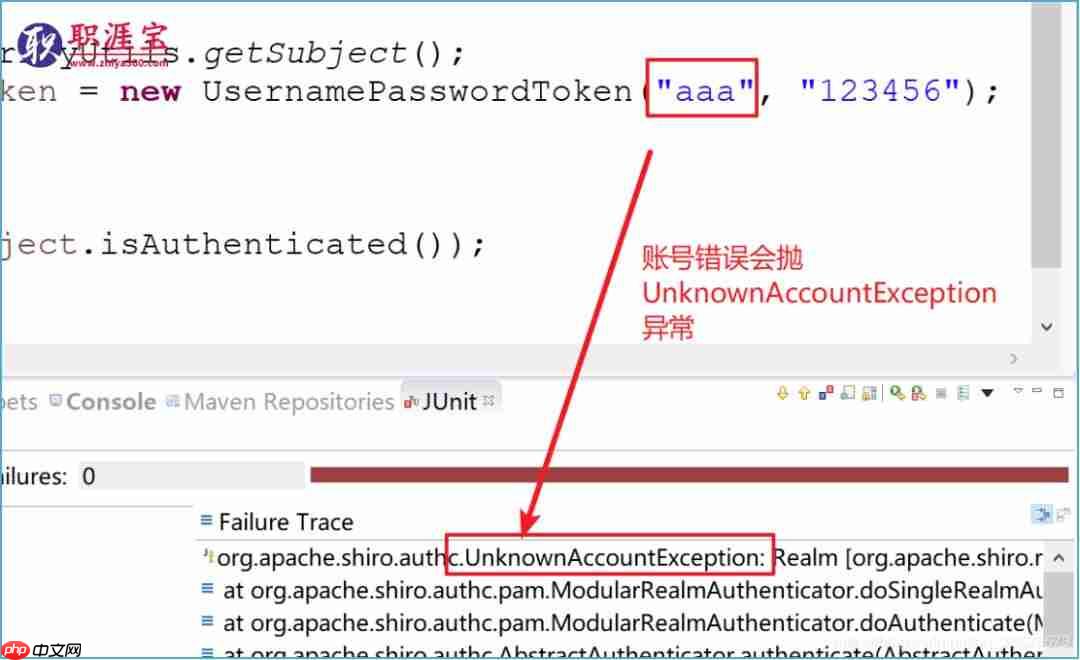
账号错误时抛出UnknownAccountException异常:
密码错误时抛出IncorrectCredentialsException异常:
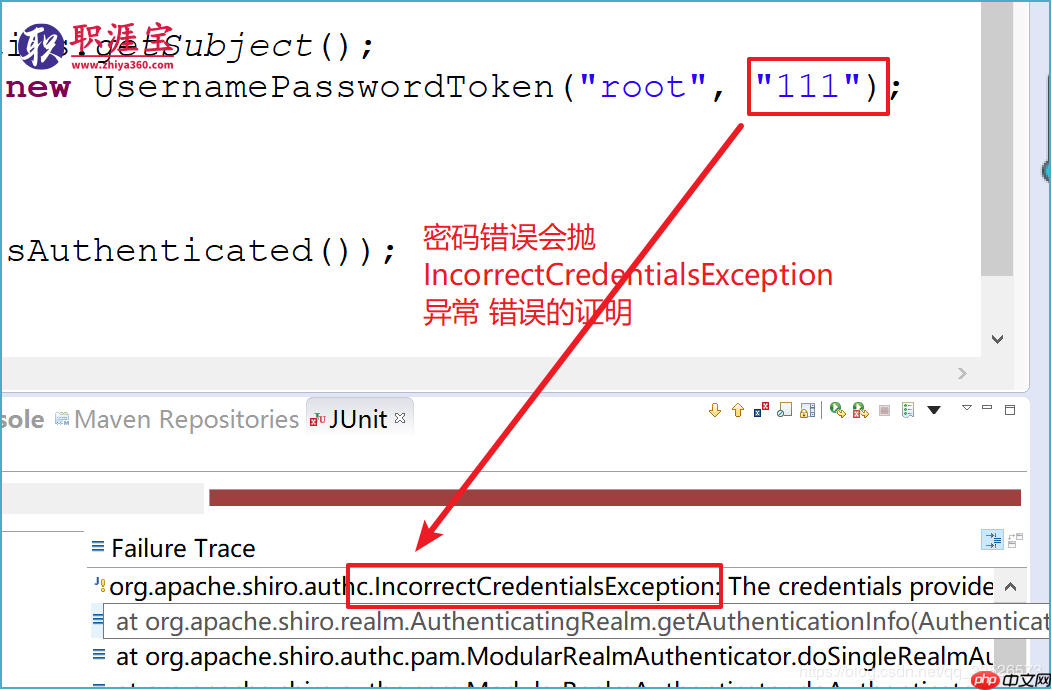
因此,代码可以调整为:
@Testpublic void test() { // 1.获取SecurityManager工厂对象 Factory factory = new IniSecurityManagerFactory("classpath:shiro.ini"); // 2.通过Factory对象获取SecurityManager对象 SecurityManager securityManager = factory.getInstance(); // 3.将SecurityManager对象添加到当前运行环境中 SecurityUtils.setSecurityManager(securityManager); // 4.获取Subject对象 Subject subject = SecurityUtils.getSubject(); AuthenticationToken token = new UsernamePasswordToken("root", "111"); // 登录操作 try { subject.login(token); } catch (UnknownAccountException e) { System.out.println("账号出错..."); } catch (IncorrectCredentialsException e) { System.out.println("密码出错..."); } // 获取登录的状态 System.out.println(subject.isAuthenticated());}
认证流程总结如下:
login方法:
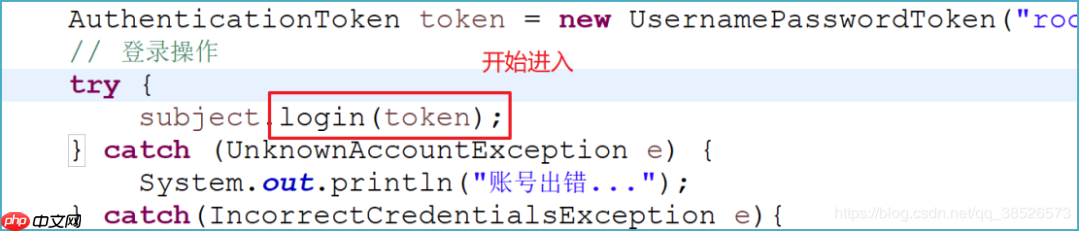
DelegatingSubject中的login方法:
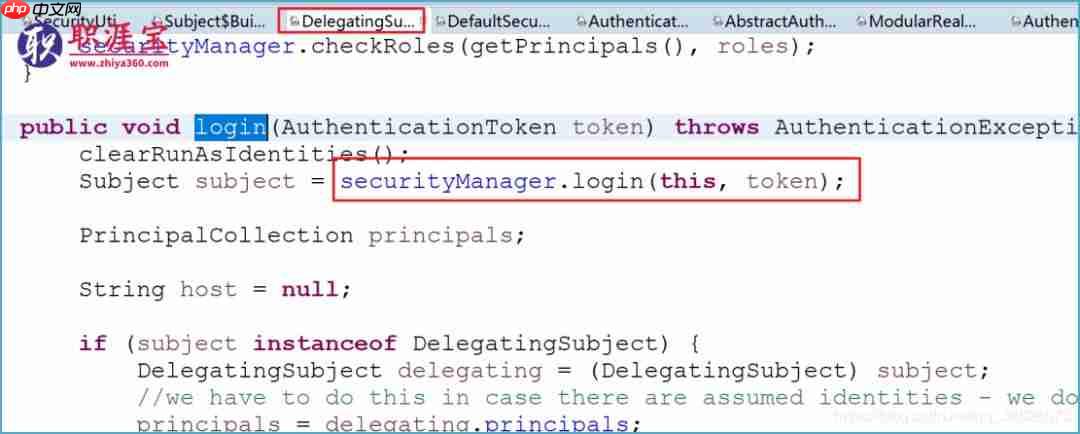
在此方法中,SecurityManager管理认证操作。继续进入DefaultSecurityManager的login方法:
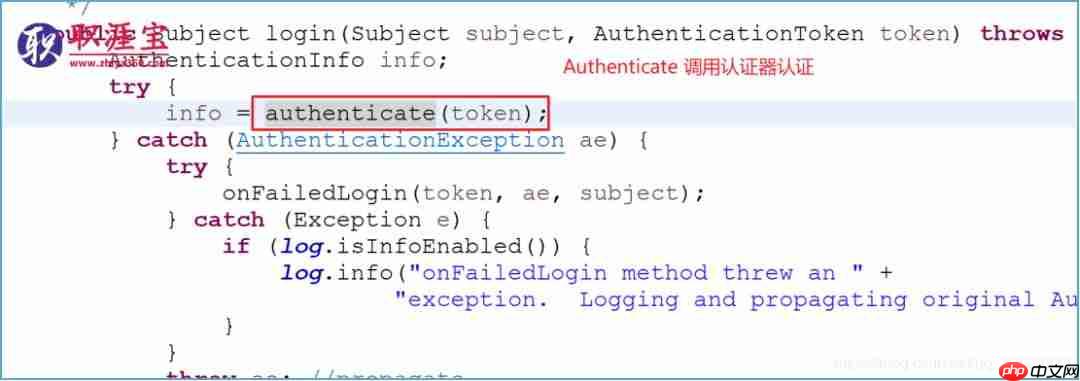
此方法中调用Authenticator进行认证:
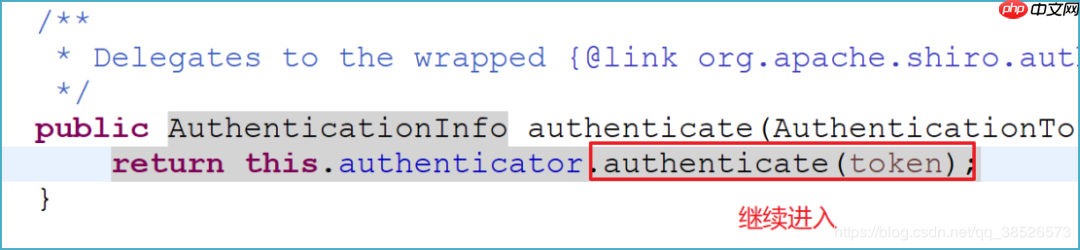
AbstractAuthenticator认证:
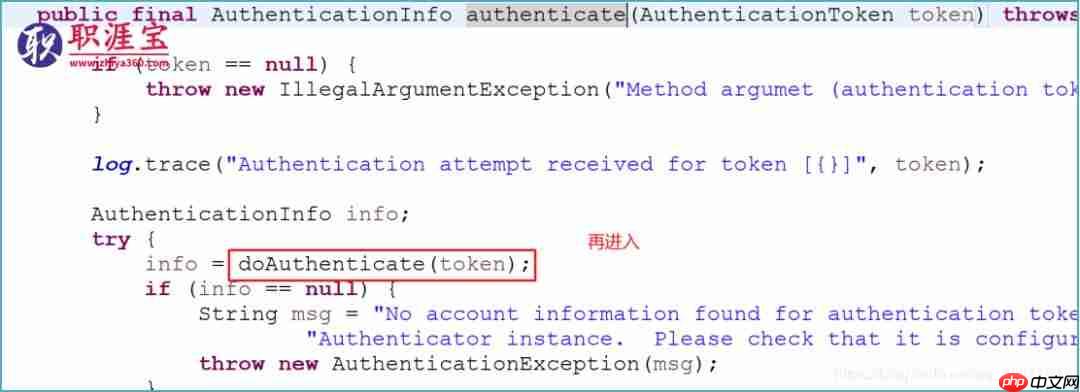
ModularRealmAuthenticator:
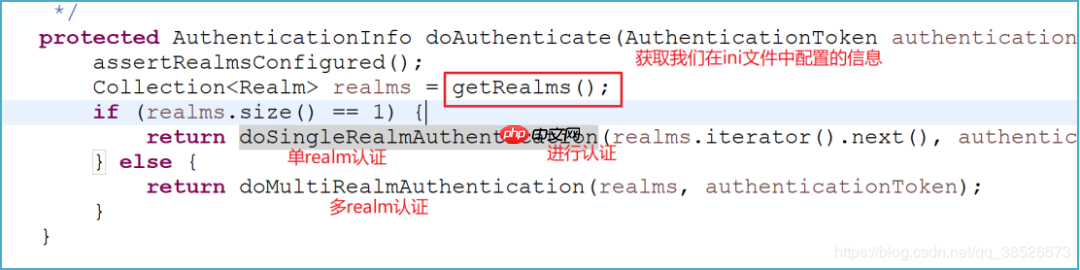
在该方法中获取ini文件中的信息,加载解析不是在此方法中进行。
AuthenticatingRealm:
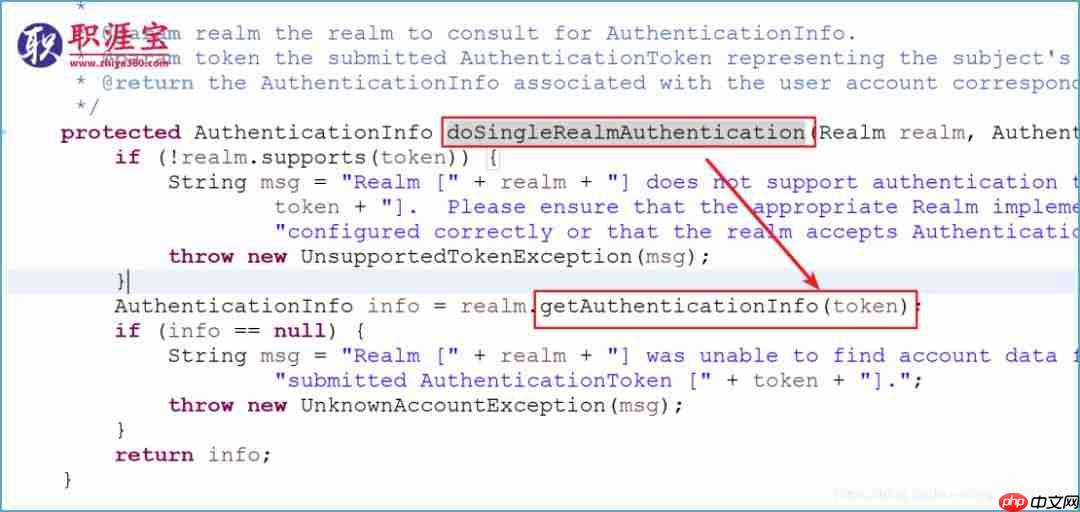
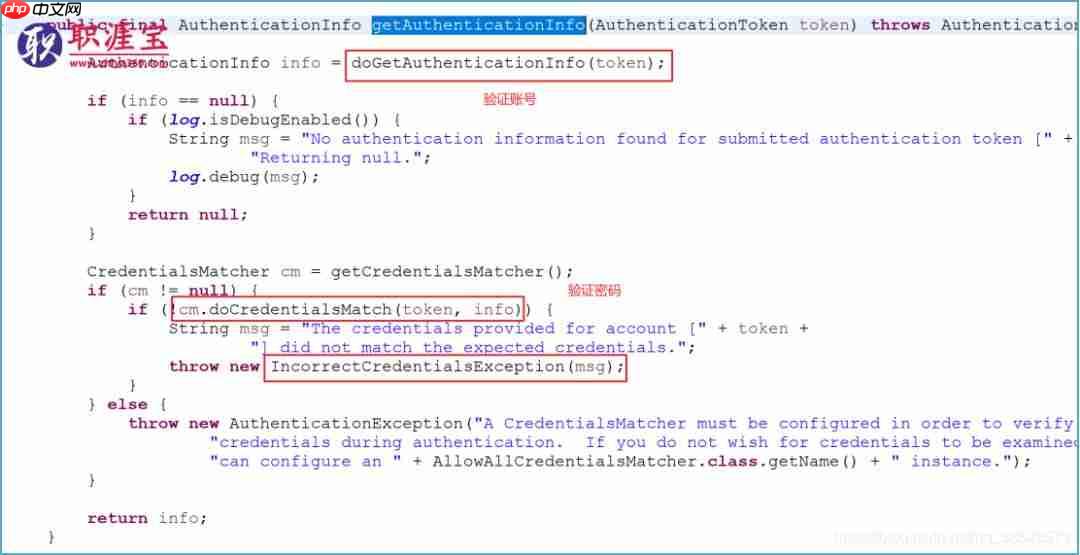
流程描述:创建token令牌,token中有用户提交的认证信息,即账号和密码。执行subject.login(token),最终由SecurityManager通过Authenticator进行认证。Authenticator的实现ModularRealmAuthenticator调用realm从ini配置文件获取用户真实的账号和密码,这里使用的是IniRealm(Shiro自带)。IniRealm先根据token中的账号去ini中查找该账号,如果找不到则给ModularRealmAuthenticator返回null,如果找到则匹配密码,匹配密码成功则认证通过。
以上就是shiro教程1(HelloWorld)的详细内容,更多请关注创想鸟其它相关文章!
版权声明:本文内容由互联网用户自发贡献,该文观点仅代表作者本人。本站仅提供信息存储空间服务,不拥有所有权,不承担相关法律责任。
如发现本站有涉嫌抄袭侵权/违法违规的内容, 请发送邮件至 chuangxiangniao@163.com 举报,一经查实,本站将立刻删除。
发布者:程序猿,转转请注明出处:https://www.chuangxiangniao.com/p/153916.html
 微信扫一扫
 支付宝扫一扫